DATA GOVERNANCE SPECIALIST
Senior Data Governance / Data Management / Cybersecurity
Location: Brussels, Belgium
Project environment: Public / Critical Infrastructure / Transport
Seniority: Senior / Expert
Experience: 7+ years
Languages: French and/or Dutch – English is an advantage
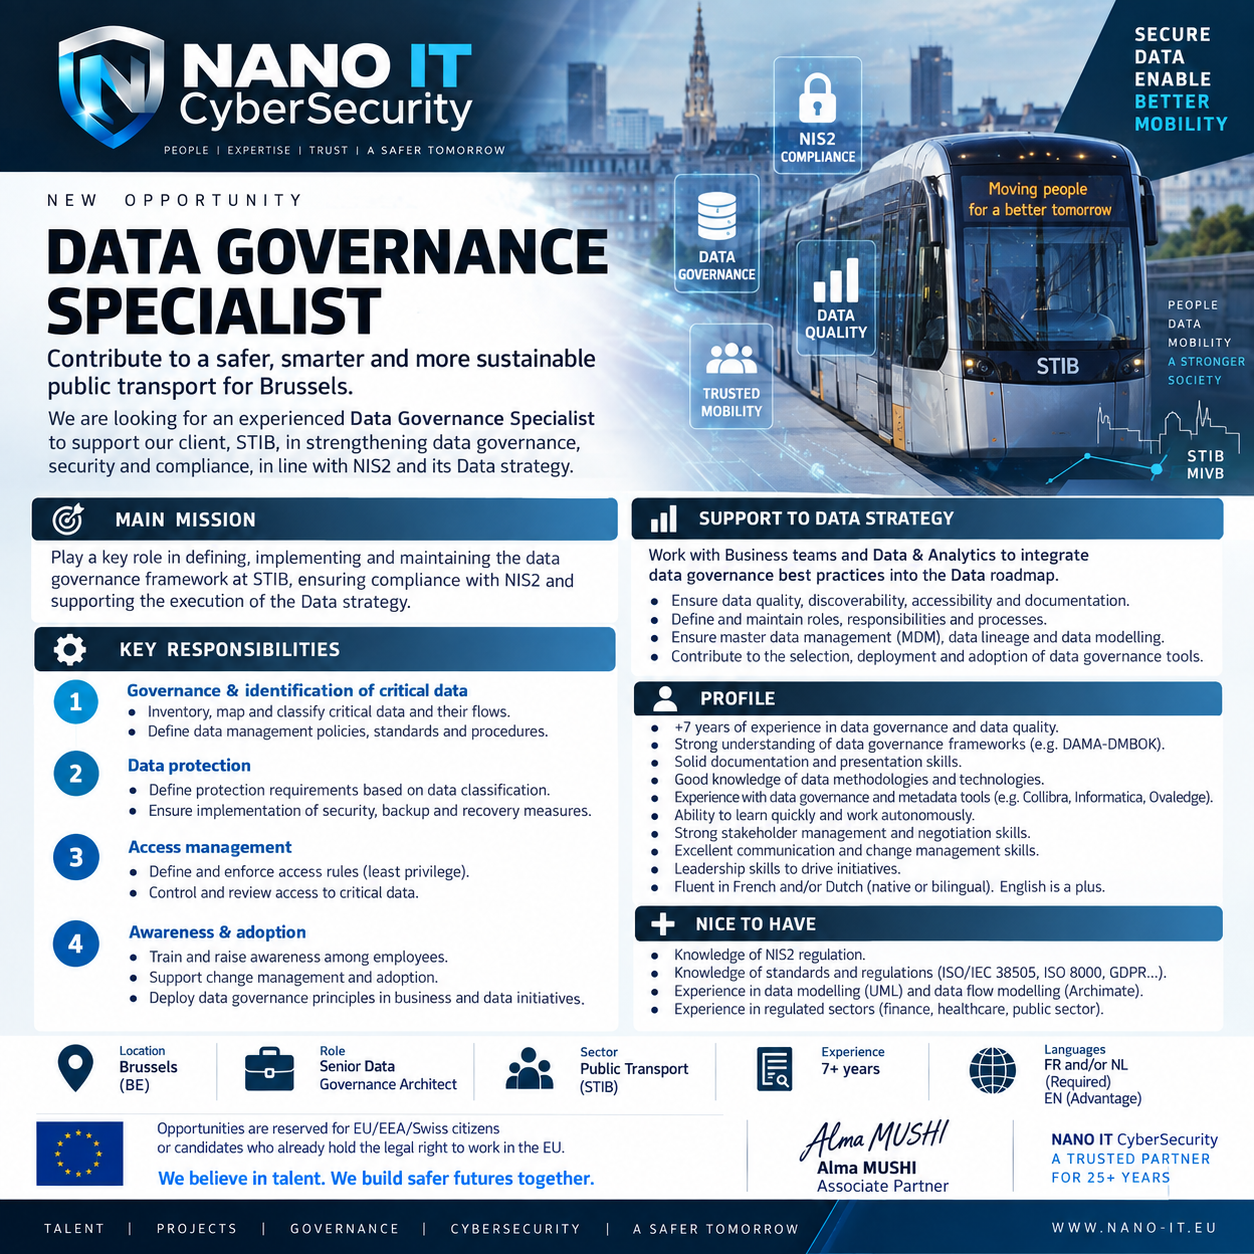
NANO IT CyberSecurity is currently selecting an experienced Data Governance Specialist for a strategic European project involving a major organisation operating within a critical and highly regulated environment.
The assignment sits at the intersection of Data Governance, Cybersecurity, Risk Management, Regulatory Compliance and Data Management.
The objective is to strengthen the organisation’s ability to identify, classify, protect, govern and effectively use its critical data while supporting the implementation of a pragmatic and sustainable Data Governance framework.
The role has a strong connection with NIS2 requirements, data protection, information security and the broader Data Strategy.
THE MISSION
The Data Governance Specialist will play a central role in defining, implementing and maintaining the organisation’s Data Governance framework.
The position requires close collaboration with stakeholders across:
- Cybersecurity / CISO
- Data Protection / DPO
- Enterprise Architecture
- Data & Analytics
- IT and Data Management
- Business stakeholders
- Document & Information Management
- Risk and Compliance
The primary focus will be on establishing effective governance and protection mechanisms for critical and sensitive data, while progressively embedding Data Governance principles into business and Data initiatives.
KEY RESPONSIBILITIES
1. Data Governance & Critical Data Identification
You will contribute to the identification and governance of the organisation’s most critical data assets.
Responsibilities include:
- Inventory and mapping of critical data.
- Identification of data owners, custodians and responsible stakeholders.
- Classification of data according to business criticality, sensitivity and regulatory requirements.
- Mapping of data flows, dependencies and relationships.
- Identification of critical data processing activities.
- Definition and maintenance of Data Governance policies, standards and procedures.
- Establishment of governance principles applicable across business and IT environments.
- Supporting the definition of data ownership and accountability.
2. Data Protection & Security
You will work closely with cybersecurity and information security stakeholders to ensure that appropriate protection mechanisms are defined for critical data.
Responsibilities include:
- Defining data protection requirements based on data classification.
- Supporting the implementation of appropriate security controls.
- Contributing to backup, recovery and resilience requirements.
- Supporting the identification of risks associated with critical data.
- Ensuring that data protection requirements are integrated into relevant projects and processes.
- Supporting alignment between Data Governance and Cybersecurity requirements.
- Contributing to regulatory compliance, particularly in relation to NIS2 and applicable data protection requirements.
3. Data Access Management
The role also covers governance of access to critical and sensitive information.
You will contribute to:
- Defining data access principles according to business requirements.
- Applying the least-privilege principle.
- Supporting access governance and accountability.
- Reviewing access rights to critical data.
- Defining rules for appropriate access, use and sharing of data.
- Working with IT and security teams to ensure that access controls are aligned with data classification.
- Supporting periodic access reviews and governance processes.
4. Data Governance Adoption & Change Management
Data Governance is not only a framework or set of policies. The successful candidate will be expected to support its adoption throughout the organisation.
Responsibilities include:
- Raising awareness of data governance principles.
- Supporting training and communication activities.
- Helping business teams understand their responsibilities regarding data.
- Promoting good practices around data ownership, quality and protection.
- Supporting organisational change and adoption.
- Explaining complex governance concepts in clear and practical terms.
- Building relationships with stakeholders across different business and technical communities.
DATA STRATEGY & DATA MANAGEMENT
A second important dimension of the role is to ensure that Data Governance becomes an integral part of the organisation’s Data Strategy.
Working with Business, Data & Analytics and IT teams, you will contribute to embedding governance principles into current and future Data initiatives.
This includes:
- Improving data quality and consistency.
- Increasing data discoverability and accessibility.
- Improving data documentation.
- Supporting metadata management.
- Establishing and maintaining governance roles and responsibilities.
- Supporting Master Data Management (MDM) initiatives.
- Contributing to Data Lineage and traceability.
- Supporting data modelling activities.
- Contributing to data architecture and governance standards.
- Ensuring governance requirements are considered within the Data roadmap.
- Supporting the selection, implementation and adoption of Data Governance tools.
REQUIRED PROFILE
We are looking for a senior professional with a strong combination of Data Governance, Data Management, stakeholder management and organisational change capabilities.
The ideal candidate should have:
- 7+ years of professional experience in Data Governance and/or Data Management.
- Strong knowledge of Data Governance principles and frameworks.
- Good understanding of DAMA-DMBOK or equivalent governance frameworks.
- Proven experience defining governance models, policies, processes and responsibilities.
- Strong experience in data quality and data management.
- Experience with metadata management and Data Governance platforms.
- Practical knowledge of tools such as Collibra, Informatica, OvalEdge or equivalent solutions.
- Good understanding of Data Management methodologies and technologies.
- Strong documentation and presentation skills.
- Excellent stakeholder management capabilities.
- Ability to work across business and technical environments.
- Strong negotiation and influencing skills.
- Ability to create and maintain an effective internal stakeholder network.
- Strong communication skills, with the ability to explain complex subjects in simple and understandable terms.
- Experience in change management and organisational adoption.
- Ability to work autonomously and take ownership of initiatives.
- Strong leadership capabilities and the ability to drive governance initiatives from definition through implementation.
NICE TO HAVE
The following experience would be considered a significant advantage:
- Knowledge of NIS2 and European cybersecurity requirements.
- Knowledge of ISO/IEC 38505 related to data governance.
- Knowledge of ISO 8000 and data quality.
- Good understanding of GDPR and data protection principles.
- Experience with UML data modelling.
- Knowledge of ArchiMate and data-flow modelling.
- Experience within regulated or critical sectors such as:
- Public sector
- Transport
- Financial services
- Healthcare
- Energy
- Critical infrastructure
- Previous experience working with CISO, DPO, Enterprise Architecture and Data Management functions.
KEY COMPETENCIES
Data Governance: Expert
Data Management: Expert
Stakeholder Management: Expert
Communication: Expert
Roadmap Management: Expert
Change Management: Advanced
Presentation: Advanced
Cybersecurity: Intermediate
LANGUAGES
French and/or Dutch: Native or bilingual proficiency
English: Professional working proficiency
WHY THIS PROJECT?
This is an opportunity to join a strategic Data Governance and Cybersecurity transformation programme where Data Governance is directly connected to:
Data → Risk → Security → Compliance → Business Resilience
The successful candidate will have the opportunity to work with senior stakeholders and contribute to the creation of a governance model designed to improve both the protection and business value of data.
The role offers a strong combination of Data Governance, Cybersecurity, NIS2, Data Management, Architecture, Risk and Change Management.
ELIGIBILITY
Opportunities are primarily intended for EU/EEA/Swiss citizens or candidates who already have the legal right to work in the relevant European country.
Candidates should indicate their current country of residence, work authorisation status, availability and preferred type of collaboration when applying.
HOW TO APPLY
NANO IT CyberSecurity is currently building its selection pipeline for this and other European projects.
If your profile matches this opportunity, please send:
- Updated CV or LinkedIn profile
- Current location
- Work authorisation / eligibility
- Availability
- Daily rate or expected remuneration, if applicable
- Preferred collaboration model
- Relevant experience with Data Governance, NIS2, ISO 27001, GDPR, GRC or Cybersecurity
NANO IT CyberSecurity
People | Expertise | Trust | A Safer Tomorrow
Selection coordinated by Alma MUSHI – Associate Partner, for NANO IT CyberSecurity.
#DataGovernance #DataManagement #Cybersecurity #NIS2 #GRC #CyberRisk #ISO27001 #GDPR #DataQuality #DataArchitecture #MDM #DataLineage #CISO #DPO #ITGovernance #Brussels #Belgium #EuropeanProjects #CyberSecurityJobs