🔐 Vulnerability Management Is Not Just an IT Issue — It Is a Governance Issue
Cybersecurity discussions often start with a technical question:
“How many vulnerabilities do we have?”
For a COMEX or CODIR, this is only the beginning.
The real questions are:
- Which vulnerabilities represent a real business risk?
- Which critical assets are exposed?
- What needs to be fixed first?
- Who is responsible for remediation?
- What is the deadline?
- What risks are being accepted?
- How do we know that remediation has actually been completed?
- Is our risk exposure improving over time?
This is where vulnerability management becomes an enterprise governance process, not simply a vulnerability scanning activity.
From detection to decision
A vulnerability scanner can identify thousands of technical findings.
But a list of CVEs is not a business risk management strategy.
The objective is to transform technical information into clear, actionable and measurable information for management.
A simple governance cycle is:
DISCOVER → DETECT → ANALYSE → CLASSIFY → PRIORITISE → REMEDIATE → VERIFY → REPORT → IMPROVE
Each step has a specific purpose.
1️⃣ DISCOVER — Know what you own
You cannot properly protect assets that you do not know exist.
Servers, workstations, applications, databases, cloud resources, network equipment, APIs, OT systems and business services should be identified and associated with appropriate ownership and business criticality.
Visibility is the foundation of cybersecurity.
2️⃣ DETECT — Find the weaknesses
Continuous or regular vulnerability assessments help identify:
- Vulnerable software
- Missing security patches
- Unsupported systems
- Misconfigurations
- Exposed services
- Weak security controls
But detection alone does not reduce risk.
3️⃣ ANALYSE — Understand the context
A CVSS score is useful, but it should not be the only factor considered.
The organization should also consider:
Technical severity + exploitability + exposure + asset criticality + business impact
A critical vulnerability on an internet-facing production system may require a very different response from the same vulnerability on an isolated test system.
4️⃣ CLASSIFY — Turn findings into risks
Vulnerabilities should be translated into understandable risk categories:
Critical | High | Medium | Low
The classification should be supported by clear criteria and agreed remediation targets.
This allows IT, Security and Management to speak the same language.
5️⃣ PRIORITISE — Focus on what matters
The objective is not necessarily to fix everything at the same time.
The objective is to ensure that the most important risks are addressed first.
This requires an agreed remediation strategy and clear escalation rules.
6️⃣ REMEDIATE — Plan and track the correction
Remediation may involve:
- Security patches
- Software upgrades
- Configuration changes
- System isolation
- Compensating controls
- Application fixes
- Technology replacement
Every significant vulnerability should have an owner, action, deadline and status.
7️⃣ VERIFY — Prove that the risk has been reduced
Closing a ticket is not the same as closing a vulnerability.
After remediation, the organization should verify that:
the vulnerability is no longer present or that an effective compensating control is in place.
This creates the evidence needed for governance, audit and compliance.
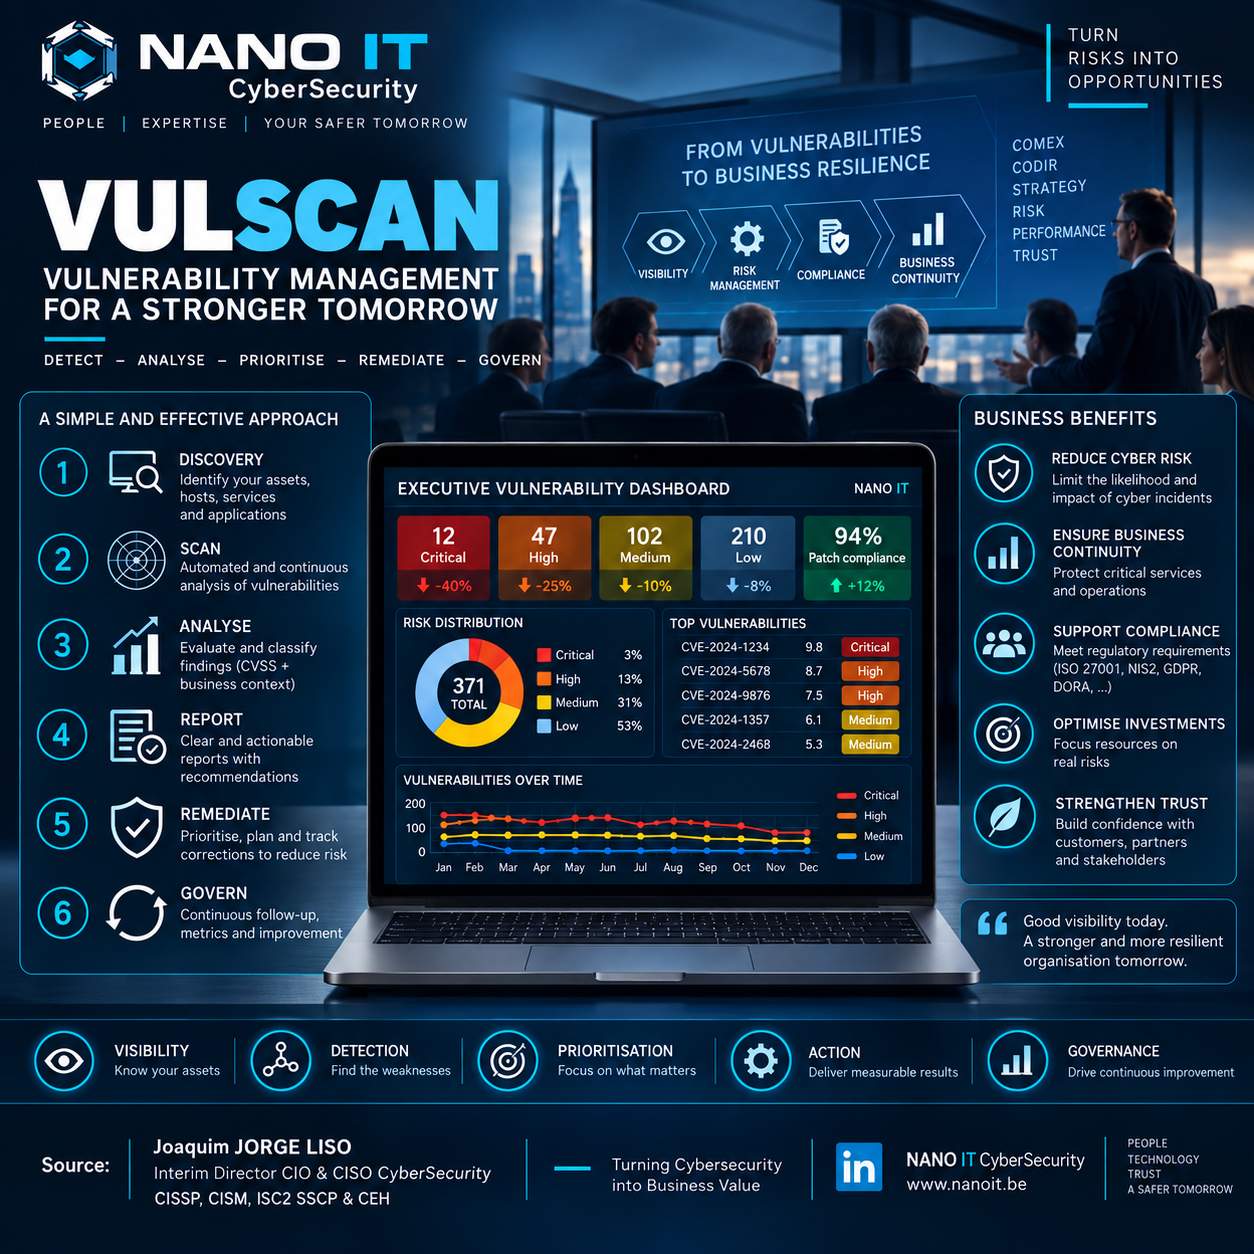
📊 What should COMEX and CODIR see?
Management does not necessarily need thousands of technical findings.
They need a clear view of the organization’s exposure and its evolution.
For example:
Critical vulnerabilities: 12
High vulnerabilities: 47
Medium: 102
Low: 210
Patch compliance: 94%
Overdue remediation: X
Assets assessed: X%
Accepted risks: X
Security exceptions: X
And, most importantly:
Are we improving?
A useful executive dashboard should show the evolution of risk over time rather than only the current number of vulnerabilities.
🗓️ Patch Management Needs Governance
Security updates should not depend on informal decisions or individual initiatives.
Organizations should establish a structured process:
Identify → Assess → Test → Approve → Schedule → Deploy → Validate → Report
And define remediation objectives according to risk.
For example, an organization may define internal targets such as:
- Critical: immediate / accelerated remediation
- High: short-term remediation
- Medium: planned remediation
- Low: maintenance cycle
These targets must be adapted to the organization’s risk appetite, regulatory requirements and operational constraints.
When remediation is not immediately possible, the exception should be formally documented, with:
Business justification → Risk owner → Compensating controls → Approval → Review date
🏢 Vulnerability Management = Enterprise IT Governance
One of the most important principles is that vulnerability management should not belong exclusively to the cybersecurity team.
It requires cooperation between:
COMEX / CODIR
↓
CIO / CISO
↓
IT Operations
↓
Application & Asset Owners
↓
Security / Vulnerability Management
↓
ITSM / Remediation Teams
Everyone has a role.
The CISO can identify and assess the risk.
IT Operations can implement the remediation.
The asset owner understands the business impact.
Management determines priorities, risk appetite and, where appropriate, accepts residual risk.
🎯 The objective is not “zero vulnerabilities”
No modern IT environment will remain permanently free of vulnerabilities.
The real objective is to establish a controlled, measurable and continuously improving risk management process.
An organization should always be able to answer:
What do we have?
What is vulnerable?
What is exposed?
What matters most?
Who owns the risk?
What are we doing about it?
When will it be resolved?
Can we demonstrate the result?
That is the difference between having security tools and having security governance.
🔐 From Vulnerabilities to Business Resilience
Effective vulnerability management contributes directly to:
Visibility — Know your IT environment
Detection — Find weaknesses
Risk Management — Understand exposure
Prioritisation — Focus resources where they matter
Remediation — Reduce exposure
Compliance — Demonstrate control and evidence
Business Continuity — Protect critical services
Trust — Strengthen confidence with customers, partners and stakeholders
Cybersecurity is therefore not only about technology.
It is about protecting the organization’s ability to operate, deliver services and create value.
Final thought for COMEX & CODIR
A vulnerability report tells you what is wrong.
Good governance tells you what matters, who must act, when it must be done, and whether the risk has actually been reduced.
That is where Vulnerability Management becomes Business Risk Management.
Source / Author
Joaquim JORGE LISO
Interim Director CIO & CISO CyberSecurity
CISSP | CISM | ISC2 SSCP | CEH
NANO IT CyberSecurity
People | Expertise | Your Safer Tomorrow
#CyberSecurity #VulnerabilityManagement #ITGovernance #CISO #CIO #RiskManagement #CyberResilience #PatchManagement #GRC #ISO27001 #NIS2 #DORA #CyberRisk #COMEX #CODIR #InformationSecurity